
 LowEndTalk member @htop recently shared the results of a honeypot that’s been setup.
I found this post quite interesting:The machine is being blasted almost every second. So, I wrote one myself, put it on the machine to collect other people’s attack behaviors. And wrote a simple web page for display, which is equivalent to a simple honeypot application. It seems that the effect is really outstanding.
A “honeypot” is a fake server, app, or system that looks legit but is actually gaslighting a potential attacker. Honeypots have many applications. For example, appearing-to-be-vulnerable servers, apps, email accounts, etc. can act as canaries for new attacks, vulnerabilities, or spam.
In this case, @htop modified the sshd binary in order to capture passwords. Normally, sshd does not record failed logins (trivia: Linux circa 0.1 logged failed users and the passwords they tried to use in syslog!). All failed attempts are then published on this web page.
If you’ve ever run a server, you probably have seen many failed logins in your syslog. Script kiddies will try hundreds/thousands/millions of IPs to see if any have accounts with poor passwords. There are different ways to combat this: turning off password authentication is the best, but you can also use fail2ban to limit attackers to only a few failed attempts before their IP is blocked. Changing the ssh port does not increase security but is often done to reduce log spam.
Looking at @htop’s collected data, we see the usual bad passwords being tried. “manager123”, “sysop”, “qwerty123!”, “00000000”, etc. I haven’t seen a “monkey1” go by yet but I’m sure it will.
Related Posts:
DreamHost Urges Affected Customers to Reset All Email and FTP Passwords
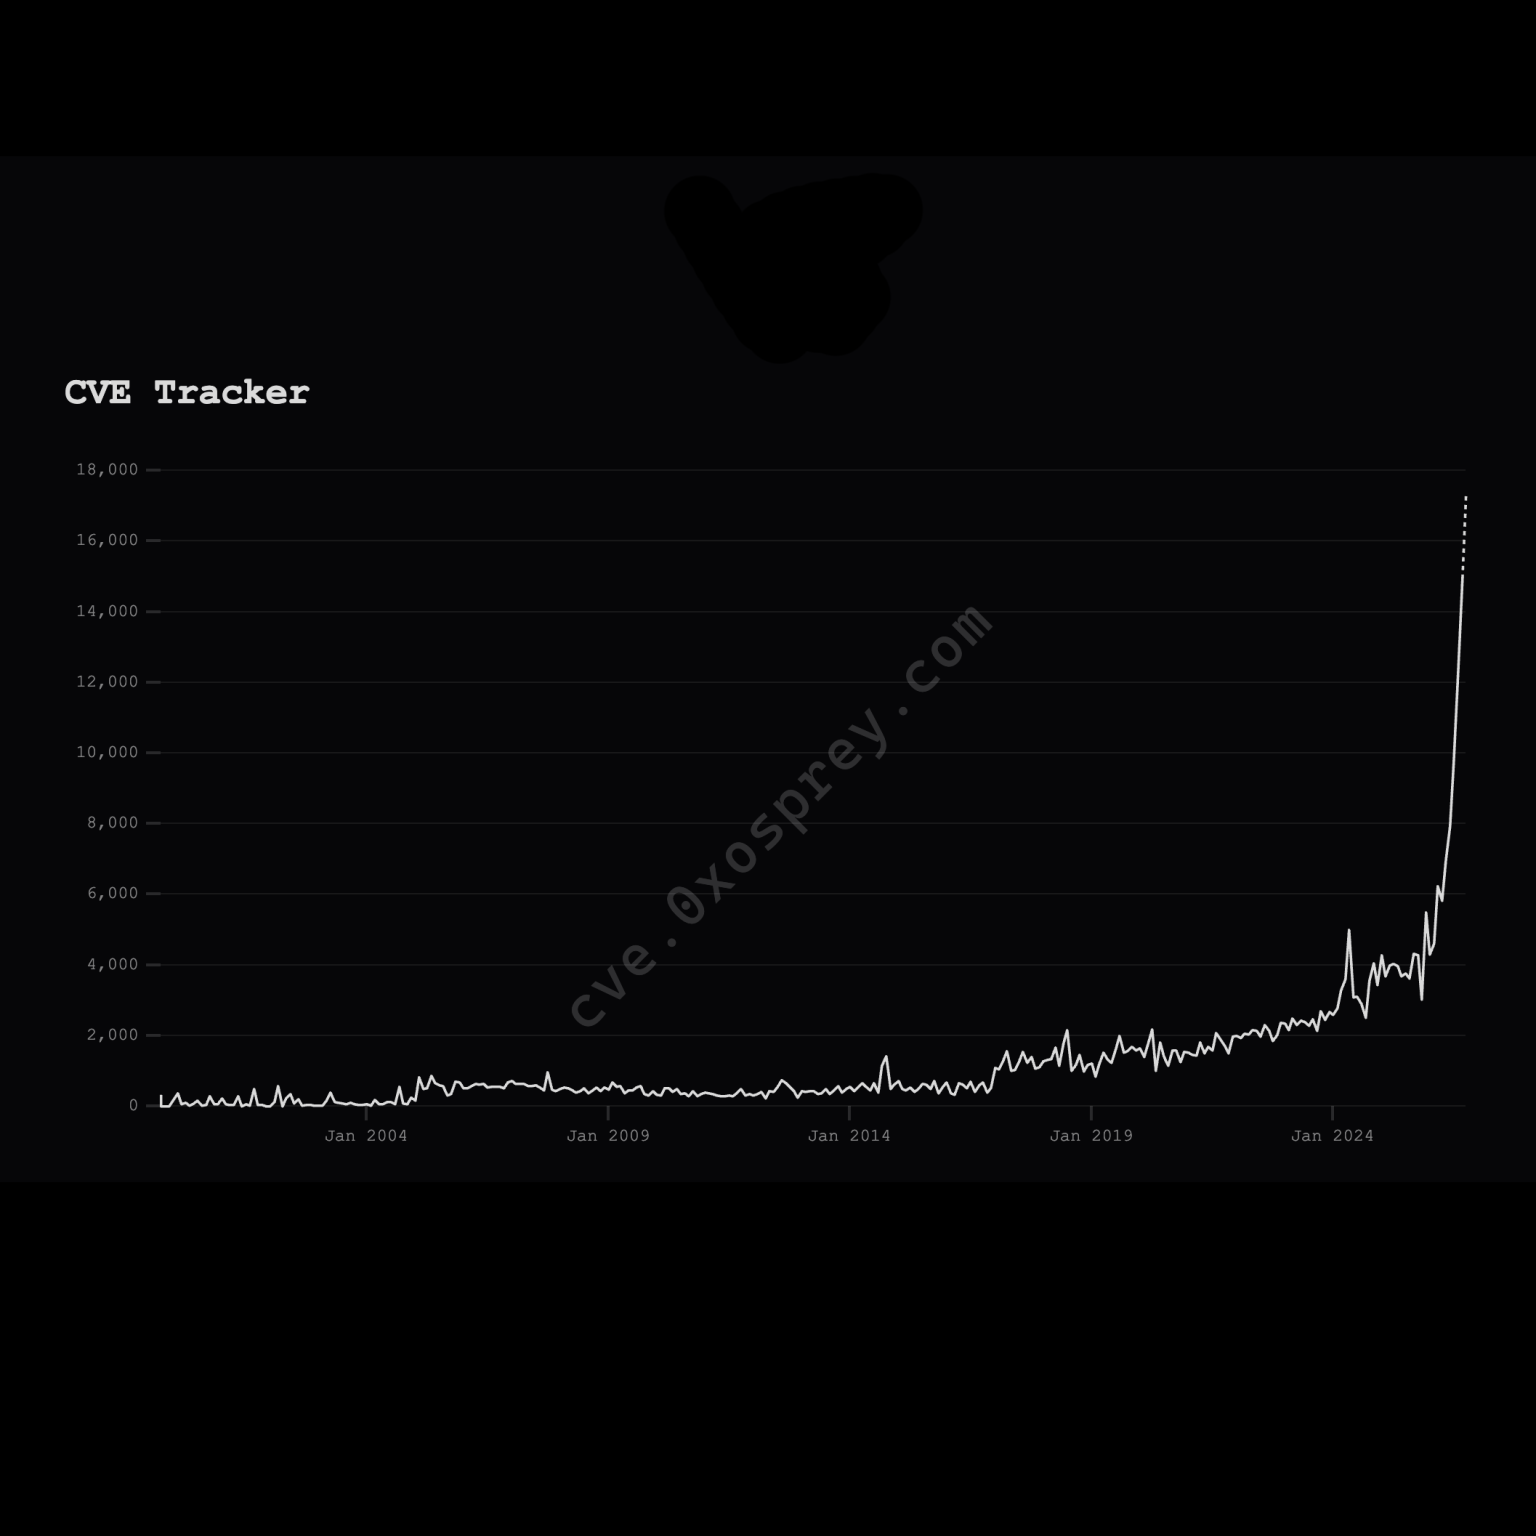
A Graph Showing Why It's Not a Fun Time to Work in IT
Patch Your PHP! The PHPopaclypse is Upon Us!
Browser Fingerprinting is Frighteningly Accurate
Forgot Your Root Password? Here's the Easy Way (and the Hard Way) to Recover It
Make Your VPS Reactive: Easily Write Scripts that Fire Automatically When Filesystem Events Occur wi...

raindog308 is a longtime community LETizen, technical writer, and self-described techno polymath. With deep roots in the *nix world, he has a passion for systems both modern and vintage, ranging from Unix, Perl, Python, and Golang to shell scripting and mainframe-era operating systems like MVS. He’s equally comfortable with relational database systems, having spent years working with Oracle, PostgreSQL, and MySQL.
As an avid user of LowEndBox providers, raindog308 runs an empire of LEBs, from tiny boxes for VPNs, to mid-sized instances for application hosting, and heavyweight servers for data storage and complex databases. He brings both technical rigor and real-world experience to every piece he writes.
Beyond the command line, raindog308 has a life-long love of German Shepherd Dogs, high-quality knives, target shooting, theology, tabletop RPGs, playing guitar, and hiking in deep, quiet forests.
His goal with every article is to help users, from beginners to seasoned sysadmins, get more value, performance, and enjoyment out of their infrastructure.
You can find him daily in the forums at LowEndTalk under the handle @raindog308.


Leave a Reply