
 Security research firm Fortbridge has released a report claiming to have discovered “multiple vulnerabilities in cPanel/WHM”.
The report states:
“Our team has found multiple vulnerabilities in cPanel/WHM during a black-box pentest, the most important one being a privilege escalation via stored XSS. Whilst disclosing these bugs to the cPanel/WHM team, we discovered the pentested cPanel account was a reseller account with the permission to edit locales, thus this is not a default setting. The XSS vulnerability which we will present is considered a feature, and it was not fixed. We will show how this “feature” can be abused to escalate privileges to root, together with the rest of our findings.”
The report is quite detailed and shows in-depth the path they take to conduct the attack.
So what do you think – is this indeed a “feature” or is it a genuine bug? cPanel has disputed the severity of this issue.
Related Posts:
DreamHost Urges Affected Customers to Reset All Email and FTP Passwords
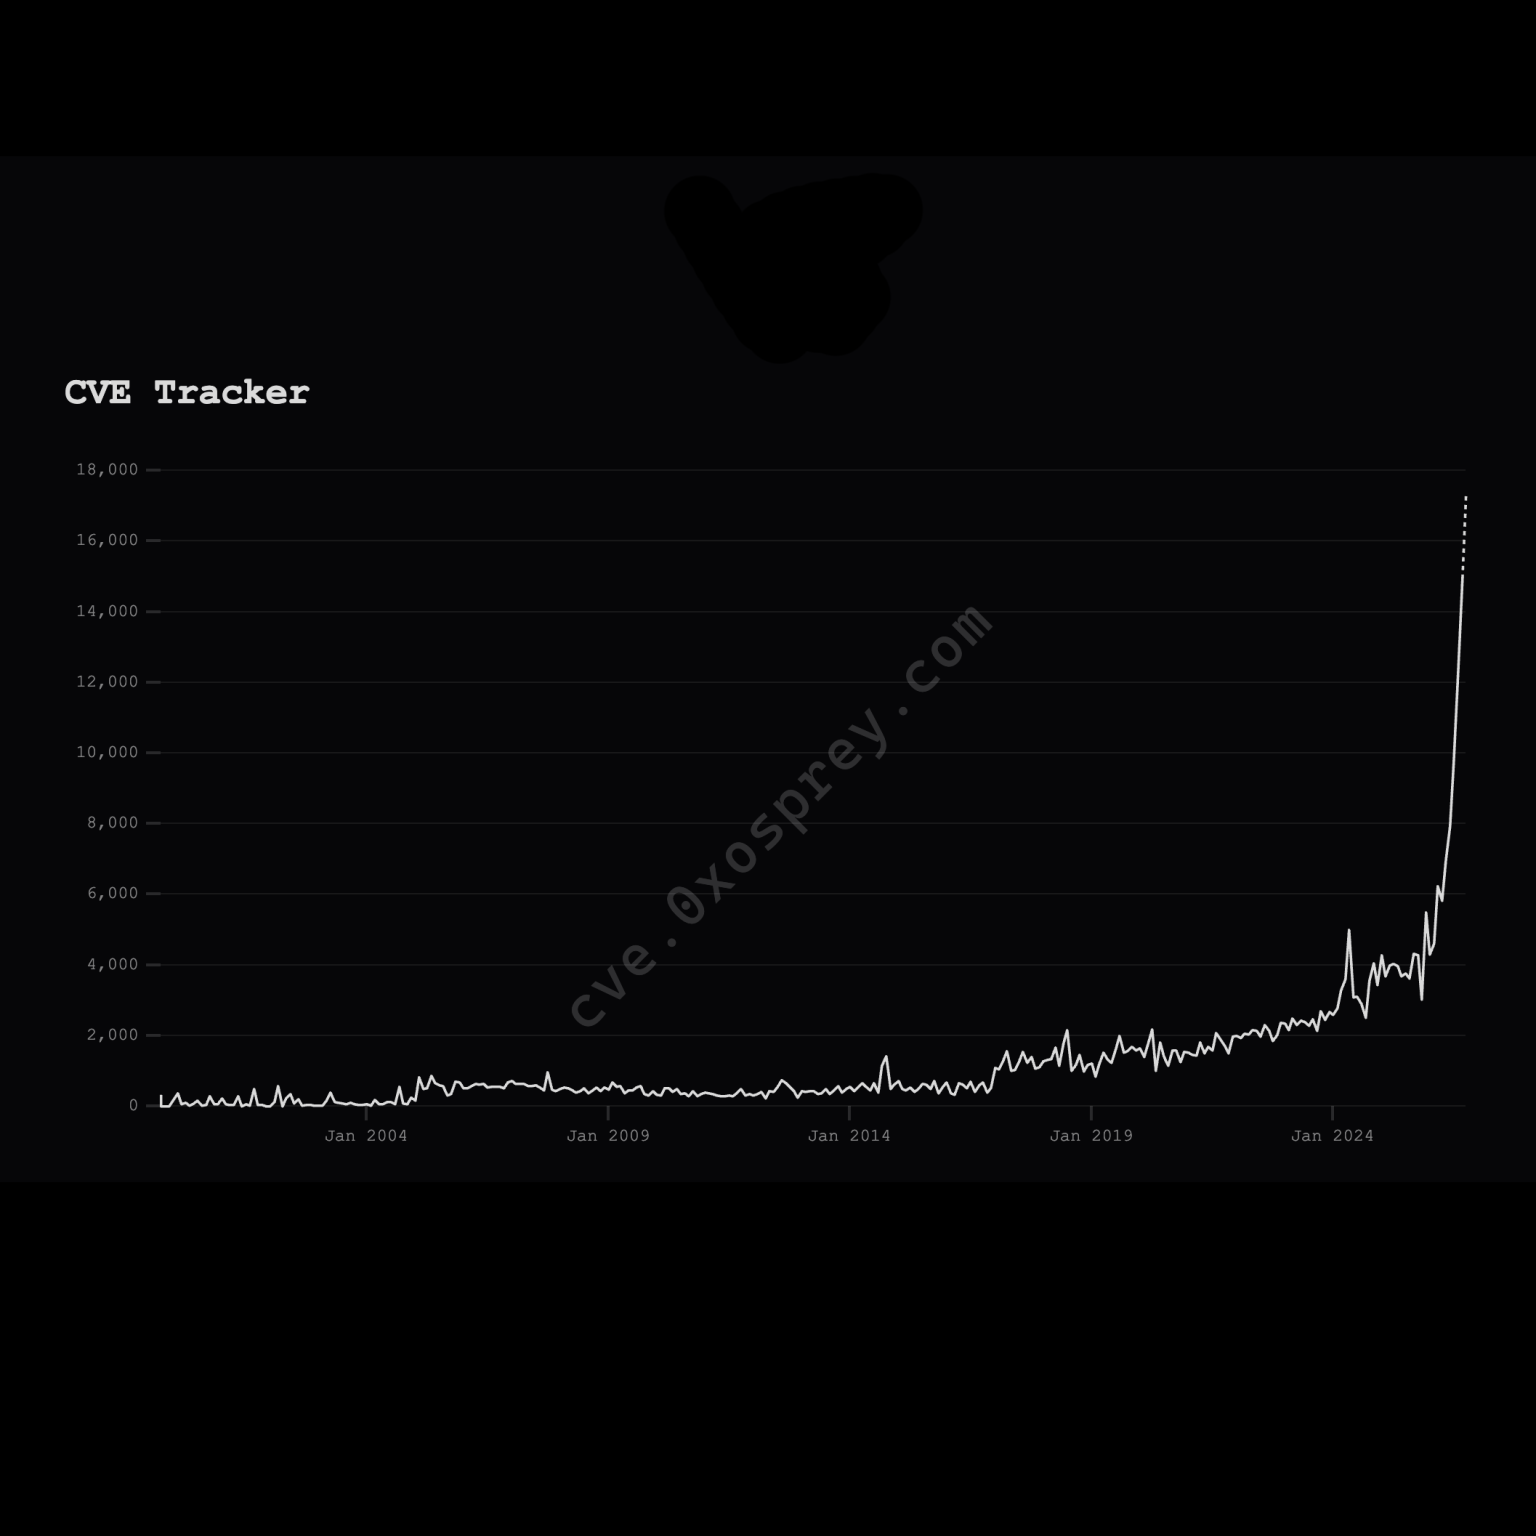
A Graph Showing Why It's Not a Fun Time to Work in IT
Patch Your PHP! The PHPopaclypse is Upon Us!
Browser Fingerprinting is Frighteningly Accurate
Yet Another cPanel and WHMCS Price Increase. But You're Getting More Value. Right? (Right?)
Debian's Unattended Upgrades is Not Enabled After You Install It - Why? Let's Deep Dive That

raindog308 is a longtime community LETizen, technical writer, and self-described techno polymath. With deep roots in the *nix world, he has a passion for systems both modern and vintage, ranging from Unix, Perl, Python, and Golang to shell scripting and mainframe-era operating systems like MVS. He’s equally comfortable with relational database systems, having spent years working with Oracle, PostgreSQL, and MySQL.
As an avid user of LowEndBox providers, raindog308 runs an empire of LEBs, from tiny boxes for VPNs, to mid-sized instances for application hosting, and heavyweight servers for data storage and complex databases. He brings both technical rigor and real-world experience to every piece he writes.
Beyond the command line, raindog308 has a life-long love of German Shepherd Dogs, high-quality knives, target shooting, theology, tabletop RPGs, playing guitar, and hiking in deep, quiet forests.
His goal with every article is to help users, from beginners to seasoned sysadmins, get more value, performance, and enjoyment out of their infrastructure.
You can find him daily in the forums at LowEndTalk under the handle @raindog308.






















Leave a Reply