
 A new vulnerability that affects many Linux systems has been revealed: Pwnkit. This attack uses a vulnerability in polkitd to allow any user to escalate his privileges to root. There are patches for major Linux systems: see the LowEndTalk thread. Thanks to @FoxelVox for posting this on LET.
It’s important to note that the vulnerability can only be used by users logged into the system. You can’t launch this attack on just any Linux box you ping on the network.
I tested on my Debian 11 systems. I find that none of my remote VMs are running polkitd, which is a user privilege management tool (previously called PolicyKit), however all of my home systems are. On my VMs, without polkitd running, the attack compiles but doesn’t work. However, it works just fine where polkitd is running.
Patch your systems ASAP!
Related Posts:
DreamHost Urges Affected Customers to Reset All Email and FTP Passwords
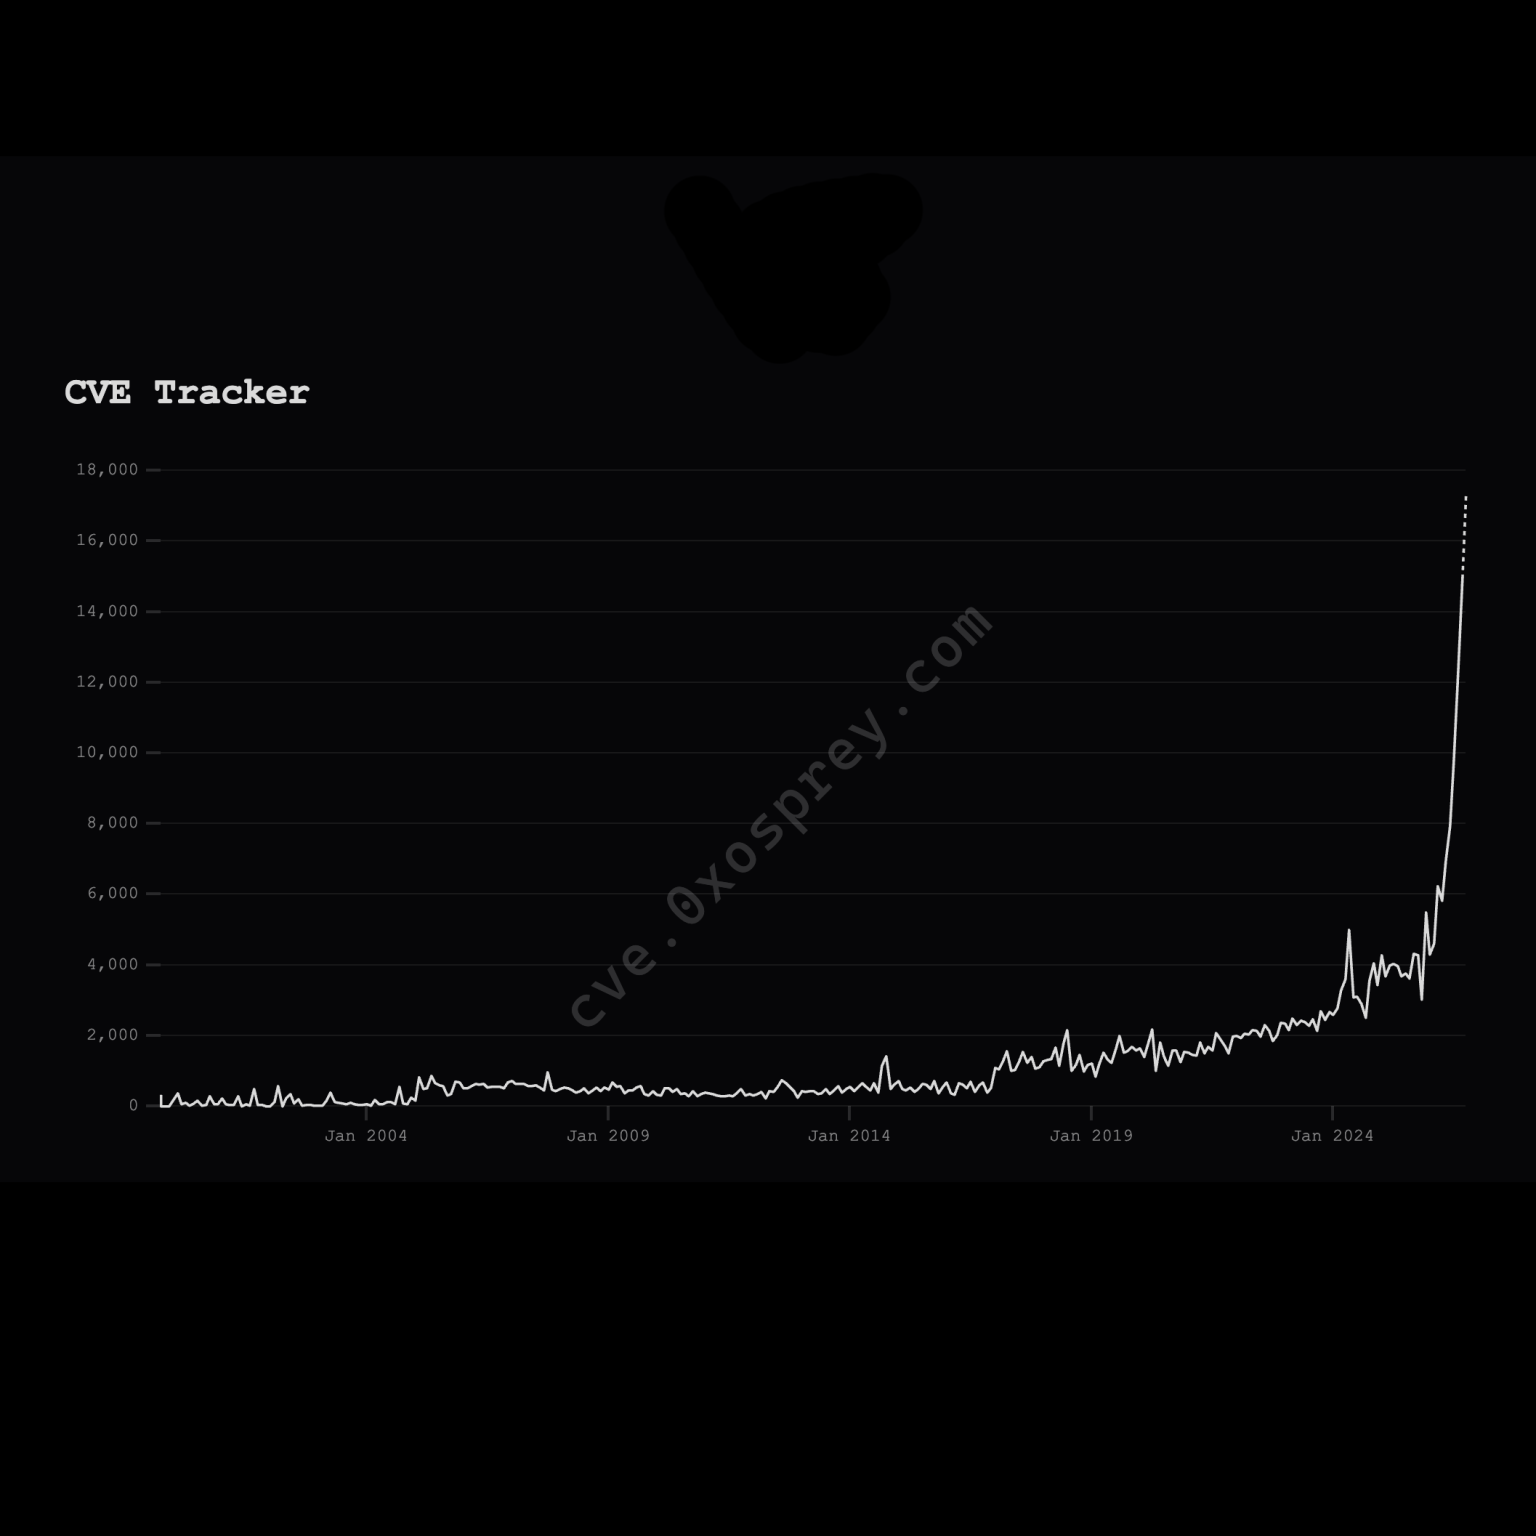
A Graph Showing Why It's Not a Fun Time to Work in IT
Patch Your PHP! The PHPopaclypse is Upon Us!
Browser Fingerprinting is Frighteningly Accurate
Forgot Your Root Password? Here's the Easy Way (and the Hard Way) to Recover It
Make Your VPS Reactive: Easily Write Scripts that Fire Automatically When Filesystem Events Occur wi...

raindog308 is a longtime community LETizen, technical writer, and self-described techno polymath. With deep roots in the *nix world, he has a passion for systems both modern and vintage, ranging from Unix, Perl, Python, and Golang to shell scripting and mainframe-era operating systems like MVS. He’s equally comfortable with relational database systems, having spent years working with Oracle, PostgreSQL, and MySQL.
As an avid user of LowEndBox providers, raindog308 runs an empire of LEBs, from tiny boxes for VPNs, to mid-sized instances for application hosting, and heavyweight servers for data storage and complex databases. He brings both technical rigor and real-world experience to every piece he writes.
Beyond the command line, raindog308 has a life-long love of German Shepherd Dogs, high-quality knives, target shooting, theology, tabletop RPGs, playing guitar, and hiking in deep, quiet forests.
His goal with every article is to help users, from beginners to seasoned sysadmins, get more value, performance, and enjoyment out of their infrastructure.
You can find him daily in the forums at LowEndTalk under the handle @raindog308.






















Dear Dreadlord. Is this still a problem if I (to my knowledge) only have one user (root) i.e. me?! Web requests come in from the www-data user, though. Thank you. Jon.C.
No they must have a shell…unless they can trick your php app into executing something on the server…