
 Earlier this month, Rackspace suffered a ransomware attack on its Hosted Exchange service. The company brought in CrowdStrike and the intrusion was limited to that service only, according to RS.
The Hosted Exchange service was a legacy product that accounted for a tiny amount of revenue (less than 1%, according to RS). In 2022, most people who want to use Outlook are on Microsoft’s Office 365. But it’s not surprising that some customers who’ve been hosting with Rackspace since before O365 existed haven’t quite got around to moving yet.
I’m sure they’ve moved now.
According to one of the suits, Rackspace’s was slow to respond to and communicate about the outage:
“That Rackspace offered opaque updates for days, then admitted to a ransomware event without further customer assistance is outrageous,” says Scott Cole, the principal attorney on the case. “Despite hundreds of data breaches every year in this country, I am receiving reports of vulnerabilities in Rackspace’s hosting environment that go back over a year. That, and a seeming lack of backup protocols is why a lawsuit like this is critical.”
At least three class-action suits have been filed.
Related Posts:
DreamHost Urges Affected Customers to Reset All Email and FTP Passwords
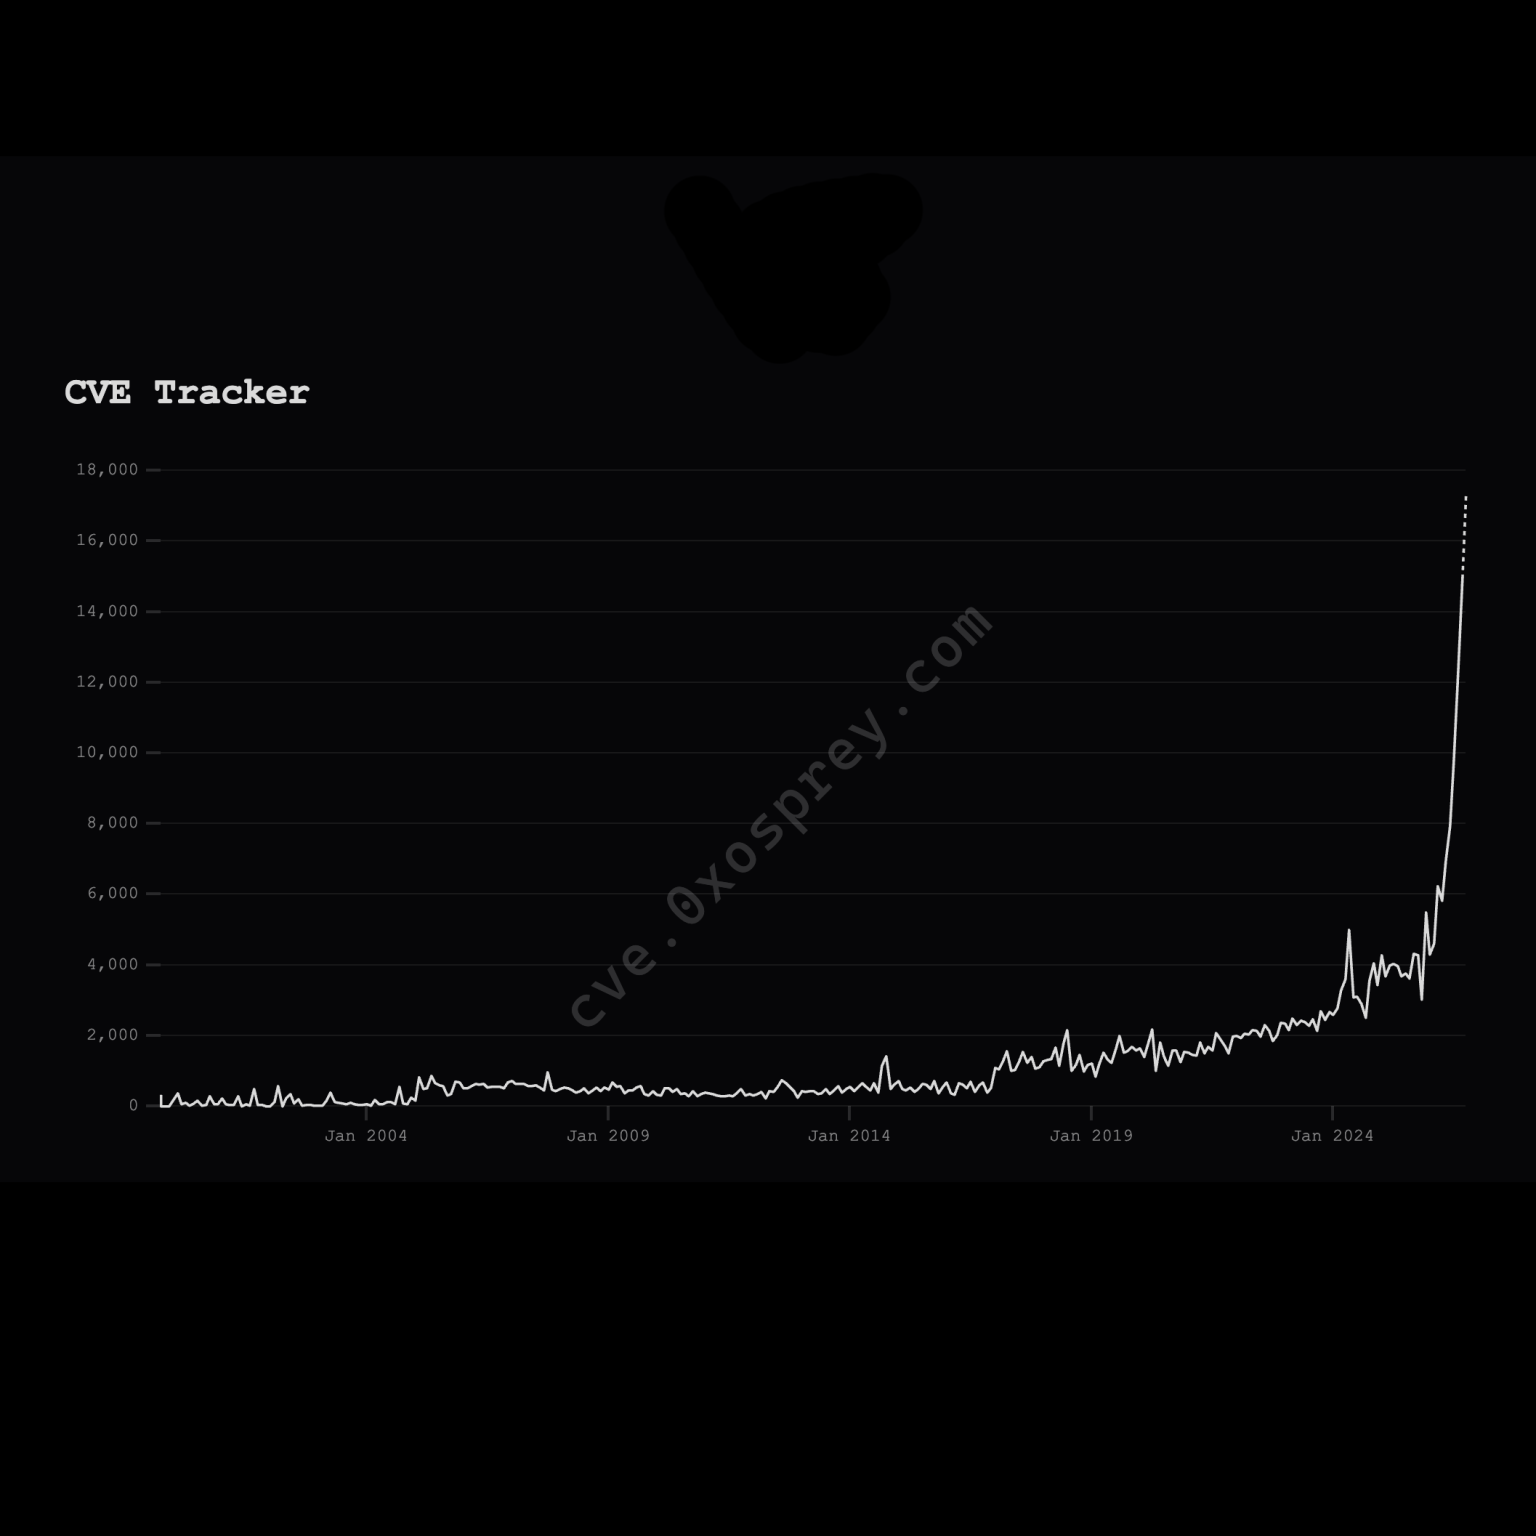
A Graph Showing Why It's Not a Fun Time to Work in IT
Patch Your PHP! The PHPopaclypse is Upon Us!
Browser Fingerprinting is Frighteningly Accurate

Microsoft Slashes the Storage that Comes with Your 365 Plan by 60%
Debian's Unattended Upgrades is Not Enabled After You Install It - Why? Let's Deep Dive That

raindog308 is a longtime community LETizen, technical writer, and self-described techno polymath. With deep roots in the *nix world, he has a passion for systems both modern and vintage, ranging from Unix, Perl, Python, and Golang to shell scripting and mainframe-era operating systems like MVS. He’s equally comfortable with relational database systems, having spent years working with Oracle, PostgreSQL, and MySQL.
As an avid user of LowEndBox providers, raindog308 runs an empire of LEBs, from tiny boxes for VPNs, to mid-sized instances for application hosting, and heavyweight servers for data storage and complex databases. He brings both technical rigor and real-world experience to every piece he writes.
Beyond the command line, raindog308 has a life-long love of German Shepherd Dogs, high-quality knives, target shooting, theology, tabletop RPGs, playing guitar, and hiking in deep, quiet forests.
His goal with every article is to help users, from beginners to seasoned sysadmins, get more value, performance, and enjoyment out of their infrastructure.
You can find him daily in the forums at LowEndTalk under the handle @raindog308.






















Whenever I come to this forum, I learn a lot. I wait for new posts from you. Thanks for sharing.
This is a concerning development—lawsuits like these raise serious questions about accountability, transparency, and risk management. It will be interesting to see how the Rackspace cases unfold and what lessons businesses can take away around security, contracts, and preparedness moving forward.