DreamHost Urges Affected Customers to Reset All Email and FTP Passwords

Something's gone wrong at Dreamhost.
Read More about DreamHost Urges Affected Customers to Reset All Email and FTP Passwords
Something's gone wrong at Dreamhost.
Read More about DreamHost Urges Affected Customers to Reset All Email and FTP Passwords
What an awful graph.
Read More about A Graph Showing Why It’s Not a Fun Time to Work in IT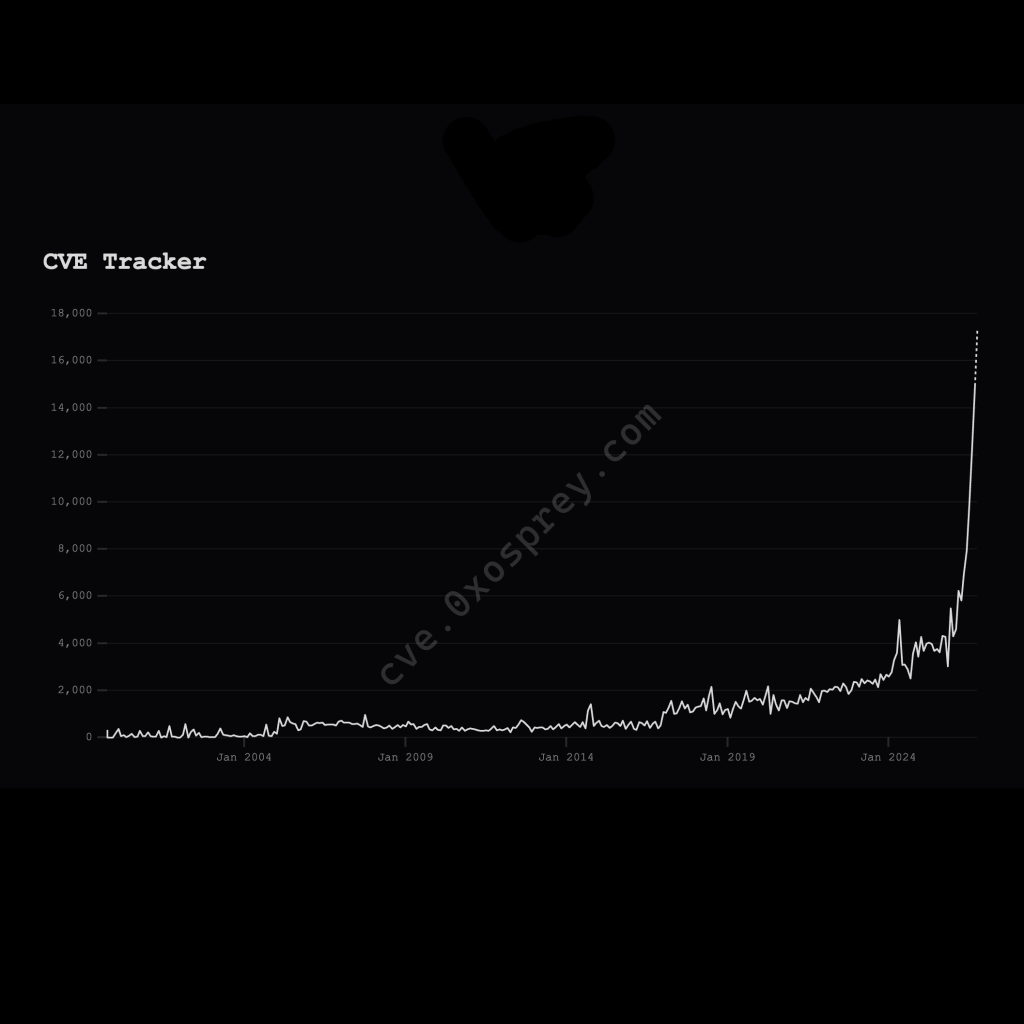
On Wednesday, October 21, 2026, a pair of PHP vulnerabilities will be unveiled at 14:00 UTC, which is 10:00 Eastern or 07:00 Pacific. News has rocketed around the Internet because these are very serious CVEs.
Read More about Patch Your PHP! The PHPopaclypse is Upon Us!
Recently, I read an article about device fingerprinting, which argues that we're in the post-tracking-cookie era. They're no longer needed, because every browser can be fingerprinted with 100% accuracy. Naturally, I had to test it.
Read More about Browser Fingerprinting is Frighteningly Accurate
I installed unattended-upgrades, but Debian wasn't upgrading. Let's get to the bottom of this puzzle.
Read More about Debian’s Unattended Upgrades is Not Enabled After You Install It – Why? Let’s Deep Dive That
I was chatting with my eldest daughter, a software dev, last night and we got on the topic of LinkedIn recruiters. Some of the tactics used by these people are familiar to anyone who's been looking for a job. But now there's a new risk.
Read More about The Contagious Interview: The Slimeyness of LinkedIn is Truly Becoming Next Level
There's a pretty grisly CVE making the rounds. It's being marketed as Januscape (CVE-2026-53359), and if you're a hosting provider, it's a headache.
Read More about Yeee-ouch! Guest-to-Host Escape Vulnerability in Linux KVM/x86
MannDude wanted to know why everything is being rewritten in Rust. Here's the answer.
Read More about ELI5: Why is Everything Being Rewritten in Rust?
The YouTube app is actually an authenticator. And that's an inconvenience.
Read More about The YouTube App is an Authenticator…and That’s a Problem
Provider says Virtualizor caused a breach. Virtualizor says no way. Providers says "video incoming..." Aaaaaaand...we're still waiting.
Read More about Whatever Happened About that Provider Who Claimed a Virtualizor Bug Caused a Breach?
Nyr's Road Warrior script makes setting up VPNs trivially easy. It's still my go-to!
Read More about Nyr’s Legendary Road Warrior Script: Still the Rock Solid Go-To for Easy VPN!
Provider says Virtualizor caused a breach. Virtualizor says no way. Providers says "video incoming..."
Read More about Provider Claims Virtualizor WHMCS Plugin Vulnerability Caused Breach. Virtualizor Doesn’t Agree."I Can Change My Password, But I Can't Change My Eyes!" Does this frequently-made comment even make sense?
Read More about If Your Biometric Data is Stolen, Should You Care? Probably Not.
xposing port 22 to the internet invites bots and brute-force attacks. There are different ways to prevent this: changing your SSH port or implementing fail2ban. There's also port knocking, which we'll implement using knockd and the knock client.
Read More about Knock, Knock: How to Shield Your VPS From Port Scanning with Port Knocking
If you're a sysadmin - and if you've got a VPS, you are - how do you learn about new security threats?
Read More about So How Exactly Do You Learn About Security Issues on Your VPS?
The SSH protocol is surprisingly complex, though the reason why it has to be makes sense once you think about everything it has to do. Using the ssh-audit package, you can audit your SSH server and tighten it up with an easy step-by-step instructions.
Read More about Tighten Up Your VPS With an SSH Audit! Let’s Look at the ssh-audit Package…Does OpenBSD Score Higher Than Debian?
Should your change your Windows RDP port? In LowEndBox's opinion, yes. Let's discuss why, and how to do it.
Read More about Hackers Love Default Windows RDP Ports: Here’s Why You Should Change Yours, and How to Do It
About 34% of the web is still powered by HTTP/1.1 and that protocol will likely come under severe attack starting on Wednesday. Get a preview of what's in store for the latest security headache.
Read More about One Third of the Web Will Stop Working in 4 Days: Massive-Scale CDN Compromise Starts Wednesday
The world is a dangerous place. Take some of the edge off by enabling Two Factor Authentication (2FA) on your WordPress sites in about 60 seconds.
Read More about How to Add Two-Factor Authentication (2FA) to WordPress in About 2 Minutes
You're busy. We get that. So let's see how you can improve your VPS security if you've only got 10 minutes to spend.
Read More about How to Keep Your VPS Safe From Hackers in Less Than 10 Minutes
Every checklist you've ever seen for securing your VPS includes "update your system regularly". But is that one of those "best practices" that is more theoretical than a real-world necessity? To be honest, it's easy to not get around to running "apt update && apt upgrade". In my experience, at least with Debian, updates rarely break things but it's always a small risk. Nevertheless, it requires remembering to do it, spending the commands run, maybe rebooting, etc. Unfortunately, history has shown time and time again that skipping OS updates can leave even the best admins wide open to disaster.
Read More about Five Times When Updating Your OS Would Have Saved You From Being Hacked
New requirements are coming for providers to Know Your Customer (KYC). Is just verifying the email address and taking a credit card enough or do they need to get into those "what was your street address four years ago" kinds of questions? Will we have to scan passports and send copies of utility bills?
Read More about Get Ready to Scan Your Passport If You Want to Buy a VM This Summer
If your server (VPS or dedicated) has been hacked, there is a simple parameter change you an make that will vastly improve its security. It takes a couple steps to login, but it will protect you against brute force attacks, keyloggers, and other attacks. And you have a couple of options.
Read More about My Server Was Getting Constantly Hacked Until I Changed This One Parameter
LowEndTalk user htop setup a honeypot to trap ssh passwords. Watch skiddies in real time!
Read More about No, ‘airforce’ is Not a Good Password: Check Out This Honeypot
MSI recently suffered a cyber attack and has issued a warning about dodgy imposter firmware that might be in the wild.
Read More about Motherboard MSI Warns of Rogue Firmware
Ezeelogin is an SSH management platform that provides two factor authentication, SAML Authentication, session recording, IAM, RBAC, PAM, and lots of other important acronyms. Community provider RackNerd recently deployed it and explains the product's benefits to providers and users.
Read More about RackNerd and Ezeelogin: Securing and Scaling SSH
"That Rackspace offered opaque updates for days, then admitted to a ransomware event without further customer assistance is outrageous," according to one attorney. Class-action lawsuits against Rackspace are popping up around the country.
Read More about Here Come the RackSpace Lawsuits
LastPass had security incidents in 2011, 2015, 2016, 2017 (twice), 2019, 2021, and twice now in 2022. Are you still using them? Why?
Read More about Just Stop Using LastPass: They’ve Been Hacked for the 9th Time
Oct 31, 2026
Oct 31, 2026
Oct 31, 2026
Oct 31, 2026
LowEndBox is a long-running resource for cheap VPS, budget hosting deals, and hosting industry news.
Our coverage blends curated offers with community insight and practical experience.
LowEndTalk is our active hosting discussion forum, while
ServerVerify helps users compare real-world server performance
and provider data.
[Learn more about our Platform]
Hostishere / Oct 30, 2026
NameBig / Oct 30, 2026
VM6 / Oct 30, 2026
tpoll / Oct 16, 2026